Microsoft Azure
Cloud solutions on Microsoft Azure that are secure, traceable, and easy to operate — with infrastructure as code and environments that are set up the same way every time.

Tools and frameworks we use
- Azure Functions
- App Service with deployment slots
- Container Apps
- Static Web Apps
- API Management
- Front Door and WAF
- Application Gateway
- Key Vault
- App Configuration
- Managed Identity
- VNets and private endpoints
- Event Hubs
- Event Grid
- SignalR Service
- Azure SQL
- Cosmos DB
- Azure Cache for Redis
- Application Insights and Log Analytics
- Azure AI Foundry
- Bicep
- Terraform
- Azure DevOps Pipelines
- Grafana
Microsoft Azure without surprises
Azure has many building blocks, and it is easy to end up with resources nobody quite knows the reason for. We build solutions where every resource has a clear owner and a clear purpose, and where the whole environment can be recreated from code. We have worked on Azure platforms with many environments and services, from Azure Functions and App Service to API Management, Front Door, and private networking.
Security is part of the foundation. Services authenticate with Managed Identity, secrets live in Key Vault, and traffic flows through private endpoints and WAF where needed.
Azure Functions, Container Apps, or App Service — how we choose
The choice of hosting affects cost, scaling, and how much the team has to operate itself. Our rule of thumb:
- Azure Functions for event-driven jobs, scheduled integrations, and workflows with Durable Functions. A good fit when load varies a lot and executions are short.
- App Service for APIs and web apps with steady traffic. Deployment slots give zero-downtime releases, and the operating model is familiar to most teams.
- Container Apps when the service is already a container, needs sidecars or several processes, or should scale to zero without being rewritten as Functions.
- Static Web Apps for frontends that do not need their own server.
We rarely recommend AKS for smaller platforms. Kubernetes offers great flexibility, but also an operational burden that only pays off when many teams share the same cluster. Whatever the choice, we use Managed Identity between services, so connection strings with secrets do not need to live in configuration.
Bicep and Terraform across many environments
As a platform grows, it becomes important that test, staging, and production are set up the same way. We have worked with versioned Bicep module libraries using template specs, where teams reuse approved building blocks instead of copying configuration, and with declarative YAML models that compile to Bicep, where each environment is described briefly and the rest is derived automatically.
For event-driven solutions we use Event Hubs, Event Grid, and SignalR Service, and for data Azure SQL, Cosmos DB, and Azure Cache for Redis. Where AI is relevant, we connect services to models in Azure AI Foundry within the same networking and access boundaries.
Typical engagements
A new solution on Azure
We choose the right services for the need, set up networking, identity, and monitoring, and deliver everything as code from the start.
Infrastructure as code
We move manually created resources into Bicep or Terraform, so changes can be reviewed, versioned, and rolled back.
Security and networking
We tighten access with Managed Identity, Key Vault, private endpoints, and WAF, without making everyday work harder for developers.
Operations and monitoring
We set up Application Insights, Log Analytics, and Grafana so the team sees errors and bottlenecks before users do.
Relevant experience
Projects and open-source work where the technology has been used in practice.
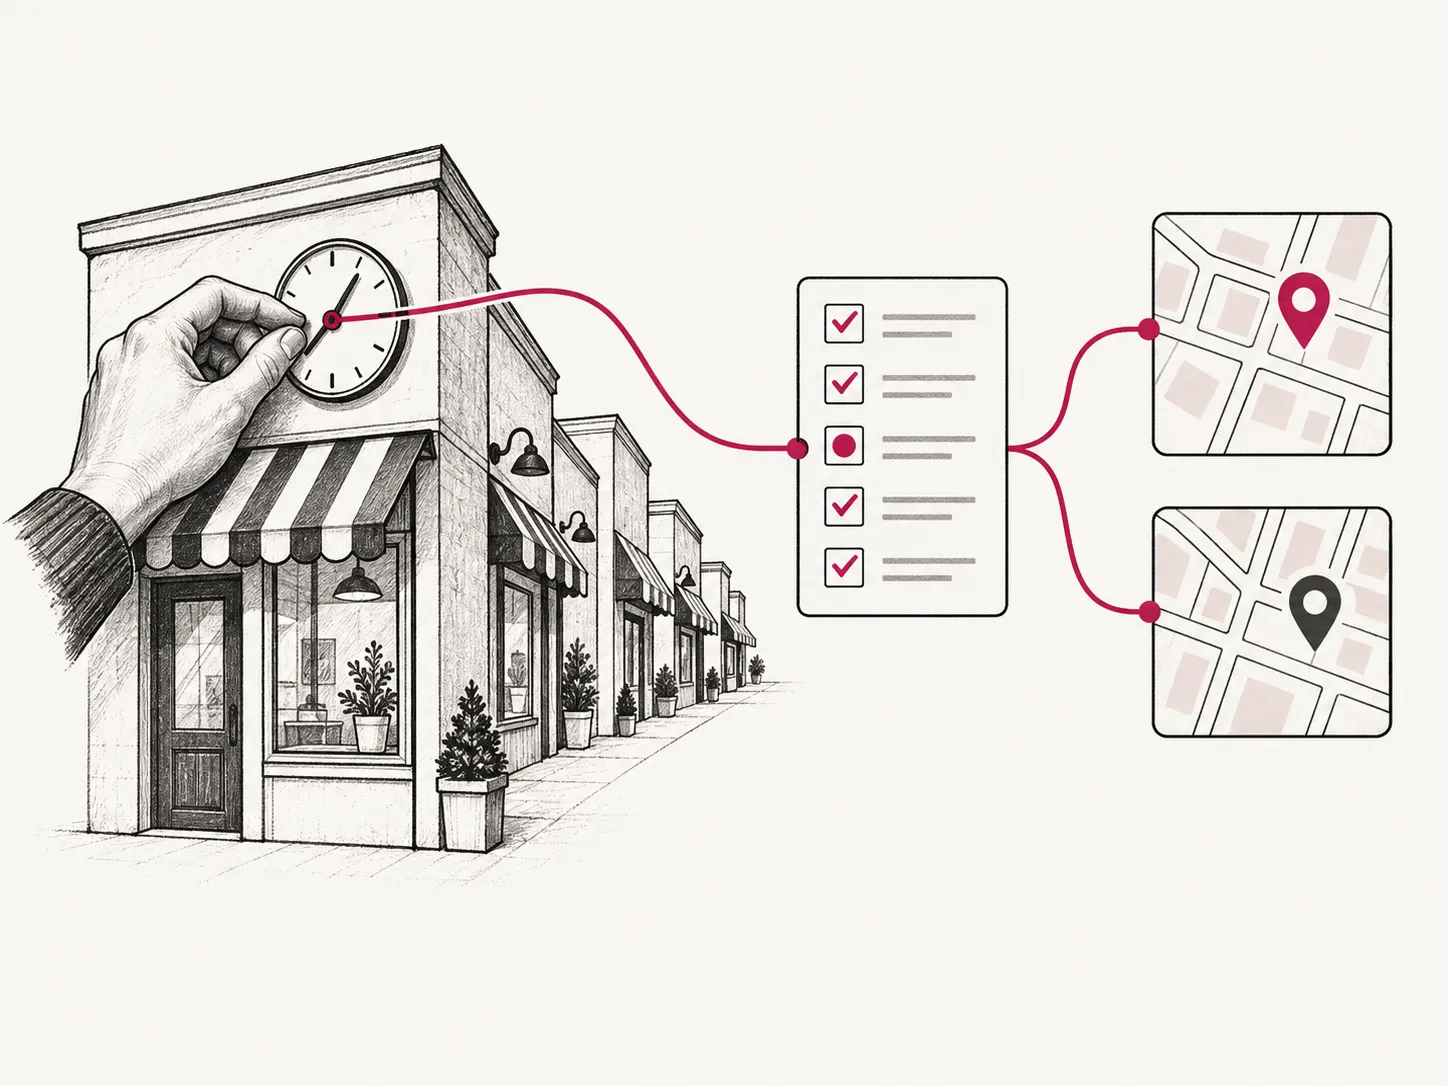
Accurate opening hours in Google and Apple Maps for hundreds of stores
We built a .NET tool on Azure that syncs opening hours for hundreds of stores to Google Business Profile and Apple Maps, checking every update first and reporting discrepancies.
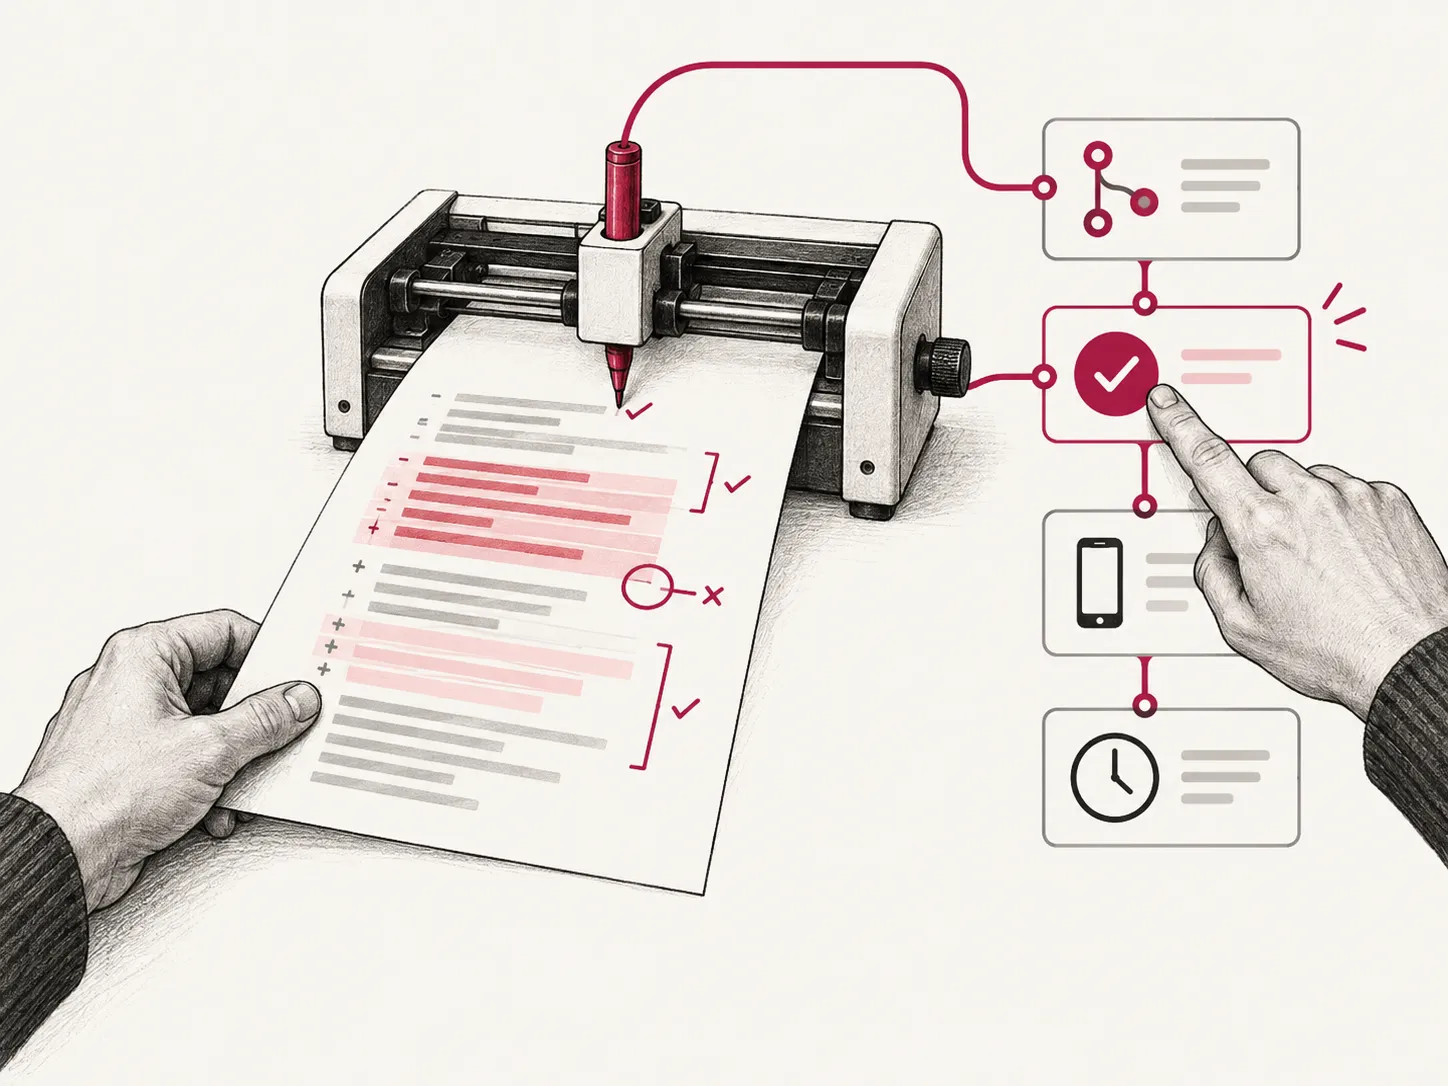
An AI assistant that reviews code and keeps the team informed
We built a TypeScript service on Azure that posts pull request, deployment, and app release notifications to Teams, and reviews code changes using language models from Azure AI Foundry.
Frequently asked questions
Do you use Bicep or Terraform?
Both. Bicep is often the simplest choice when everything runs on Azure, while Terraform works well when several cloud providers or services outside Azure need to be managed in one place.
Can you take over an existing Azure environment?
Yes. We start by reviewing resources, access, costs, and deployment routines, then propose a plan for what to move into code first.
How do you handle multiple environments?
We describe environments as code and deploy them through pipelines with approval before production. Among other things, we have worked in a setup where a declarative YAML model compiles to Bicep across several environments.
Do you help reduce Azure costs?
Yes. We look at sizing, scaling rules, and service choices, and propose changes based on actual usage from Azure monitoring.
How quickly can you start?
Get in touch with a short description of what you need, and we will respond with an assessment of scope and when we can contribute.
Related technologies
Part of the service: Backend development and integrations
DevOps and CI/CD
Pipelines, containers, release automation, and monitoring, from a single app to platforms with hundreds of pipelines.
Read moreTypeScript and Node.js
Backend services, integrations, and internal tools in TypeScript and Node.js, from REST APIs to build and release automation.
Read more.NET and C#
APIs, microservices, and integrations in C# and .NET, from new services to modernising older codebases to .NET 10.
Read moreNeed help with Microsoft Azure?
Tell us briefly about the product, the team, or the system. We will respond with a practical suggestion for the next step — a complete delivery, senior capacity in your team, or technical advice.
- Phone
- +47 920 50 946
- Location
- Oslo, Norway